The page to forward to your security lead
Erasure standards, what happens to a drive that cannot be wiped, physical destruction, chain of custody, and the per-drive wiping report.
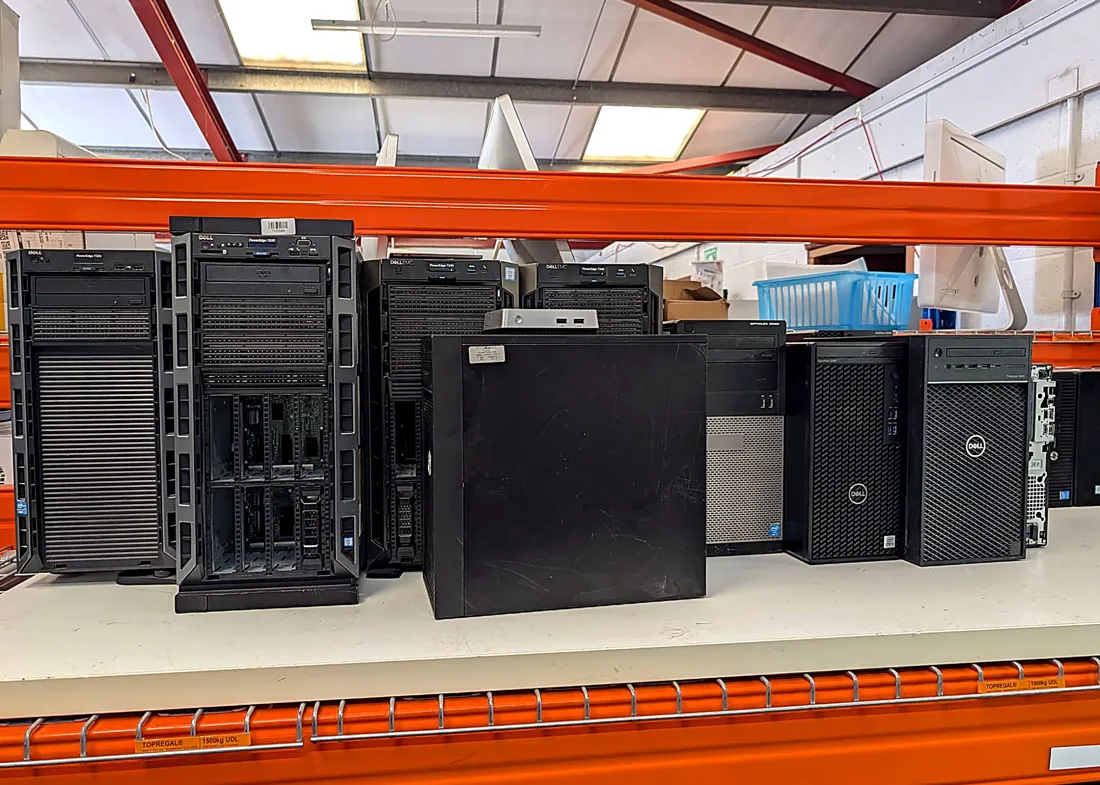
Secure
Erased to NCSC guidance and reported drive by drive.
Certified
ADISA ITAD Essentials Certified. ISO 9001, 14001 and 27001, and a registered waste carrier.
Award-winning
Excellence in Sustainability, Thames Valley Chamber of Commerce.
Documented
An itemised asset list and data destruction certificate for every collection.
The standard
Erased in line with current NCSC guidance
Every drive is erased in line with current guidance from the National Cyber Security Centre, formerly HMG Infosec Standard 5. The erasure software we use is ADISA certified.
When a drive cannot be erased
It is physically destroyed. So is any drive where you would rather have destruction than a wipe. If you have specific requirements for how destruction is carried out, tell us and we will confirm what we can do before you book.
What you receive
A Certificate of Data Destruction with a manifest listing every device by serial number, within 28 working days. Alongside it, a data wiping report listing each drive and the wiping method used on it.
Where responsibility sits
You remain the data controller for any personal data on the equipment. Liability sits with you until collection and with us from the point of collection onwards.
Before we arrive you are responsible for releasing BIOS passwords, cloud locks and mobile device management enrolments.
Download a redacted certificate
Related reading
Can data ever truly be deleted?
The data sanitisation experiment
Independently audited · Silver level
ADISA ITAD Essentials Certified
ADISA Certification is a UK certification body that specialises in data sanitisation and IT asset disposal. Its auditors spent two days testing how we collect, track, secure and erase retired IT.
The audit covers six areas of risk: logistics, asset management, chain of custody, physical security, data sanitisation and process control. Day two was a live technical test of our data sanitisation, covering our tools, procedures, quality control and the competence of our team.
Check our certification on ADISA’s register · Read the announcement
Why it matters
What happens when disposal goes wrong
Send this page to whoever needs to sign it off
No obligation. If we are not the right fit we will say so.